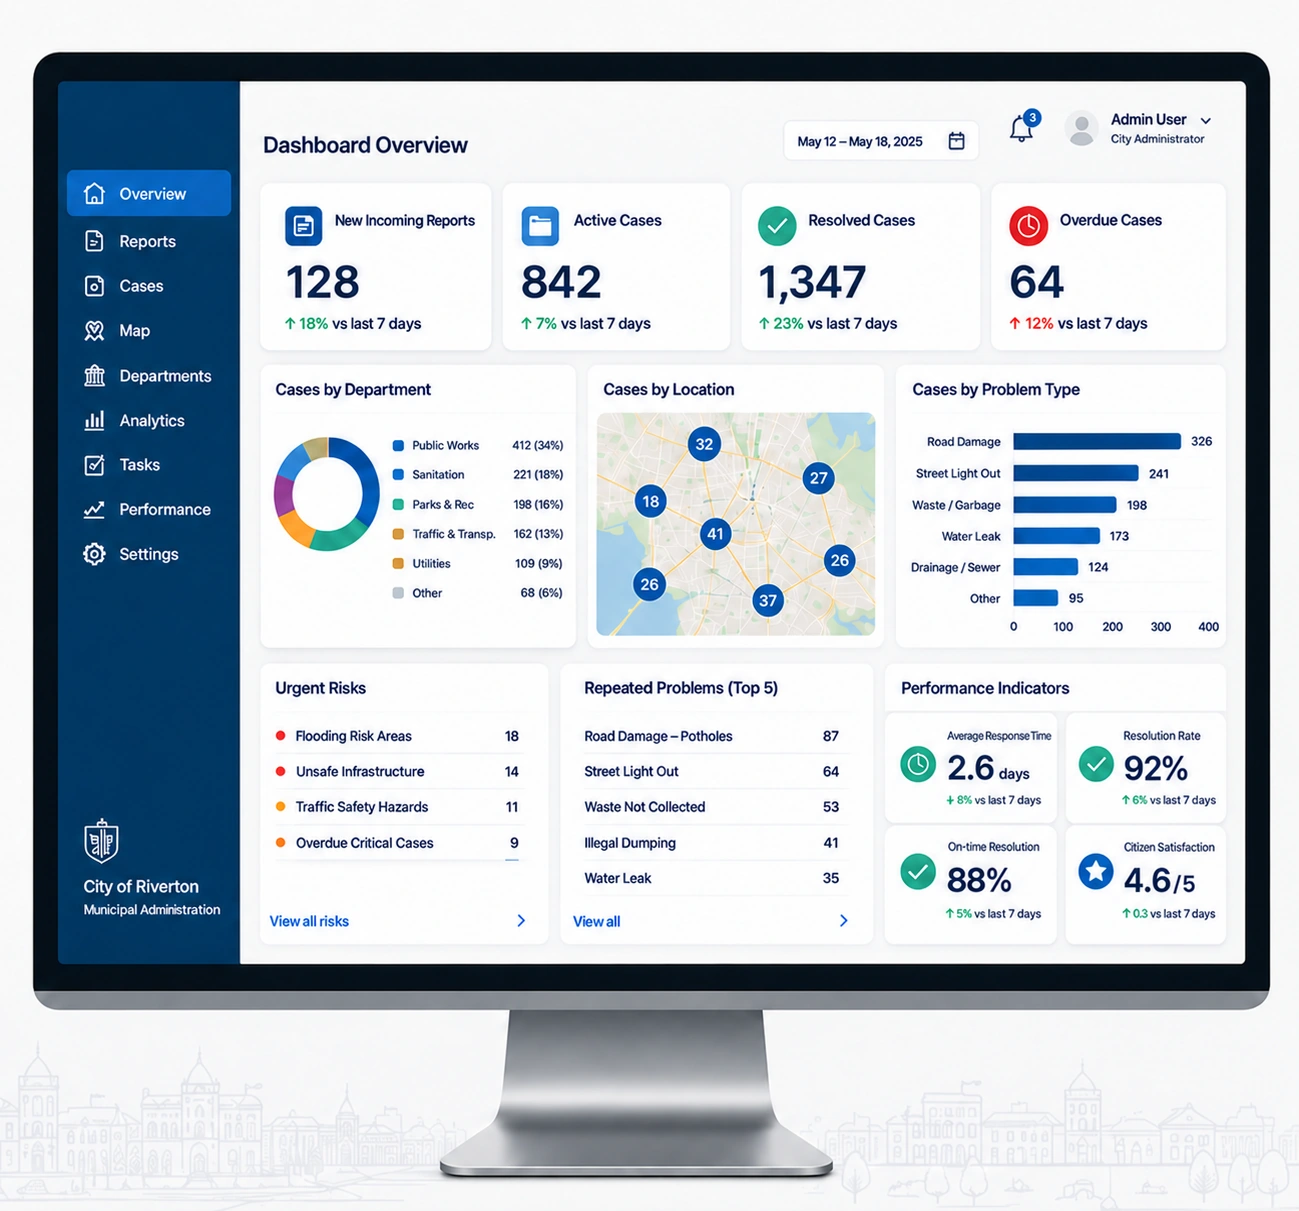
Leadership oversight.
Agree the organizational and reporting scope that authorized leadership needs to review.
Security & Data
A city-wide management system needs clear rules for access, information and continuity. Bring your IT, procurement and data protection teams into the discussion from the start.
Access and responsibility
Leadership, service teams and administrators have different responsibilities. Define who needs to see information, who can act and who maintains the system.
Data and hosting
The institution should understand where the service operates, how its information is handled and what happens throughout the deployment lifecycle.
Confirm the configuration and contractual responsibilities for the deployment being evaluated.
Data protection and the GDPR
We design MyCivic with the GDPR's principles in mind, including keeping personal data to what the service needs. Before we handle any real personal data for your institution, a written agreement on data protection will be in place, and we will support your institution's data protection impact assessment where one is needed.
Your institution decides on its residents' requests and publishes its own privacy notice before its service opens. The written agreement will set out what each party is responsible for, including the use of any outside provider and how we would tell your institution about an incident.
Access follows each person's role, and each institution's information is kept separate from every other institution's. Outside organizations that carry out the work see only the jobs given to them and are not shown who reported the problem.
Statistical breakdowns by area or category hold back very small counts, to reduce the risk of anyone being singled out.
Each step in a case is recorded, with who took it and when. The case history is protected against tampering.
Before a resident's photo is saved, hidden details in the file, such as camera information, are removed. Photos are shown only to people authorized to see them.
How long data is kept, and whether your institution wants it returned or deleted when a pilot or contract ends, will be agreed in writing before any real use.
The details for each deployment are agreed with the institution and written into its agreement.
Technical review
Request current documentation for the proposed deployment. Security assurances and service commitments should be supported by evidence and reflected in the agreed scope.
Review the deployment design, authentication approach, roles and administration model.
Review hosting, processing responsibilities, retention, export and supporting agreements.
Review service levels, maintenance, backups, recovery and incident handling.
Review interfaces, migration, dependencies, acceptance criteria and configuration changes.